Share hashed, read-only views with a passwordless user made for Churney. Six steps, or let Claude do them.
At a glance: Read-only on hashed views · Personal data hashed in your cluster · No passwords exchanged
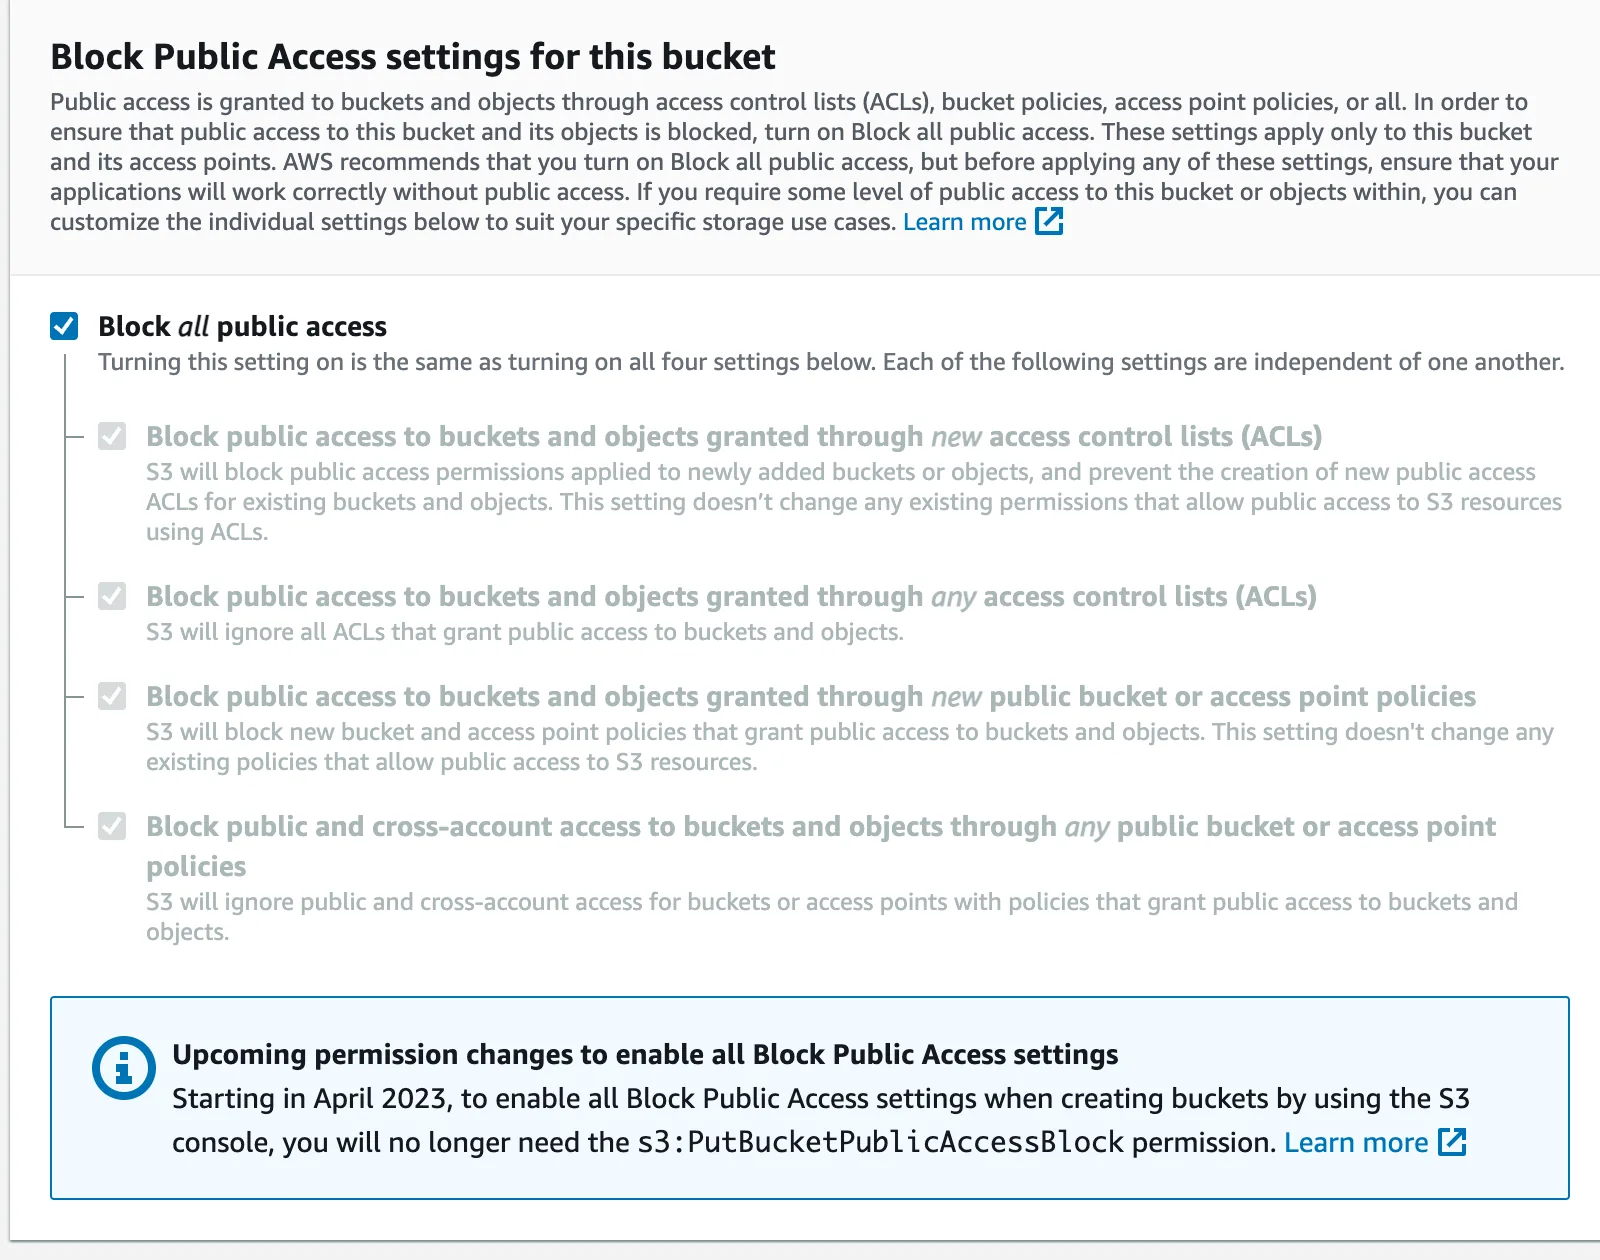
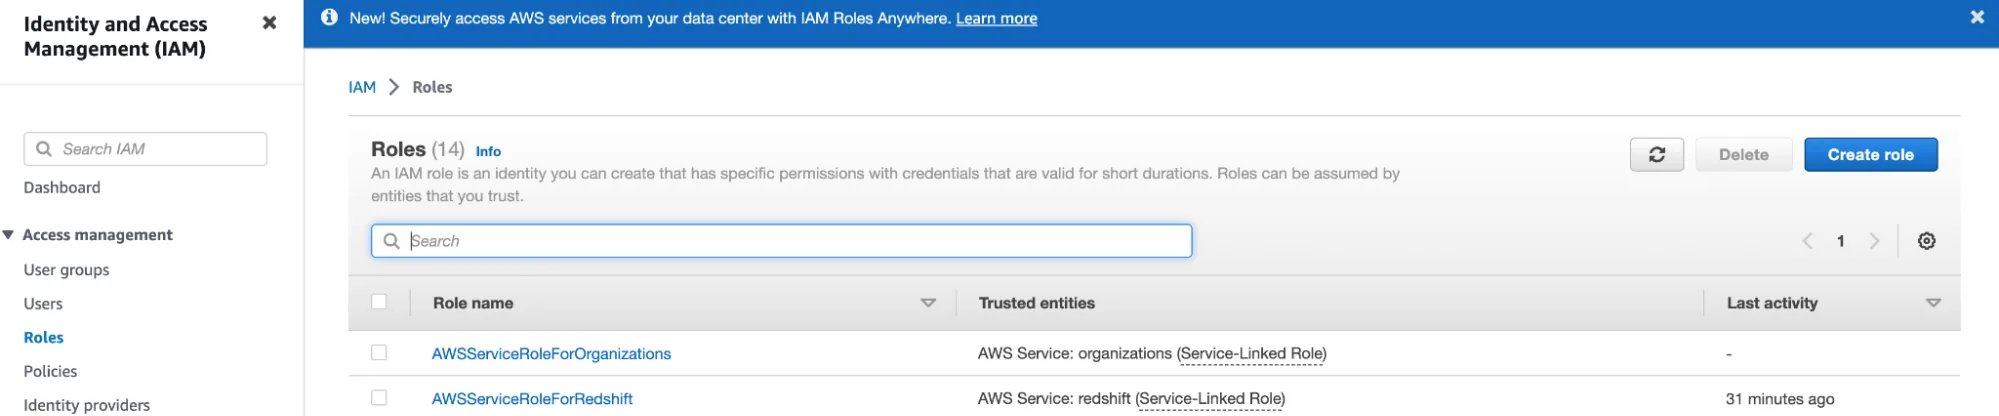
Churney connects to your cluster from one static IP as a database user without a password, using short-lived credentials from an IAM role that trusts only Churney. We read the hashed views in a churney schema and unload them to an S3 bucket in your account. Anything that identifies a person is hashed before it leaves your cluster.
Then create one view per table you share. Each view hashes the columns that can identify a person, such as email, phone, name, birthday and street address. Redshift has no * EXCEPT, so list the other columns you share. Cast TIME columns to text: Redshift cannot unload TIME to Parquet.
Fill in your names below and copy the SQL. Rather we write the views for you? Use the List your columns tab and send us the result.
The database, the user churney, and the views in churney
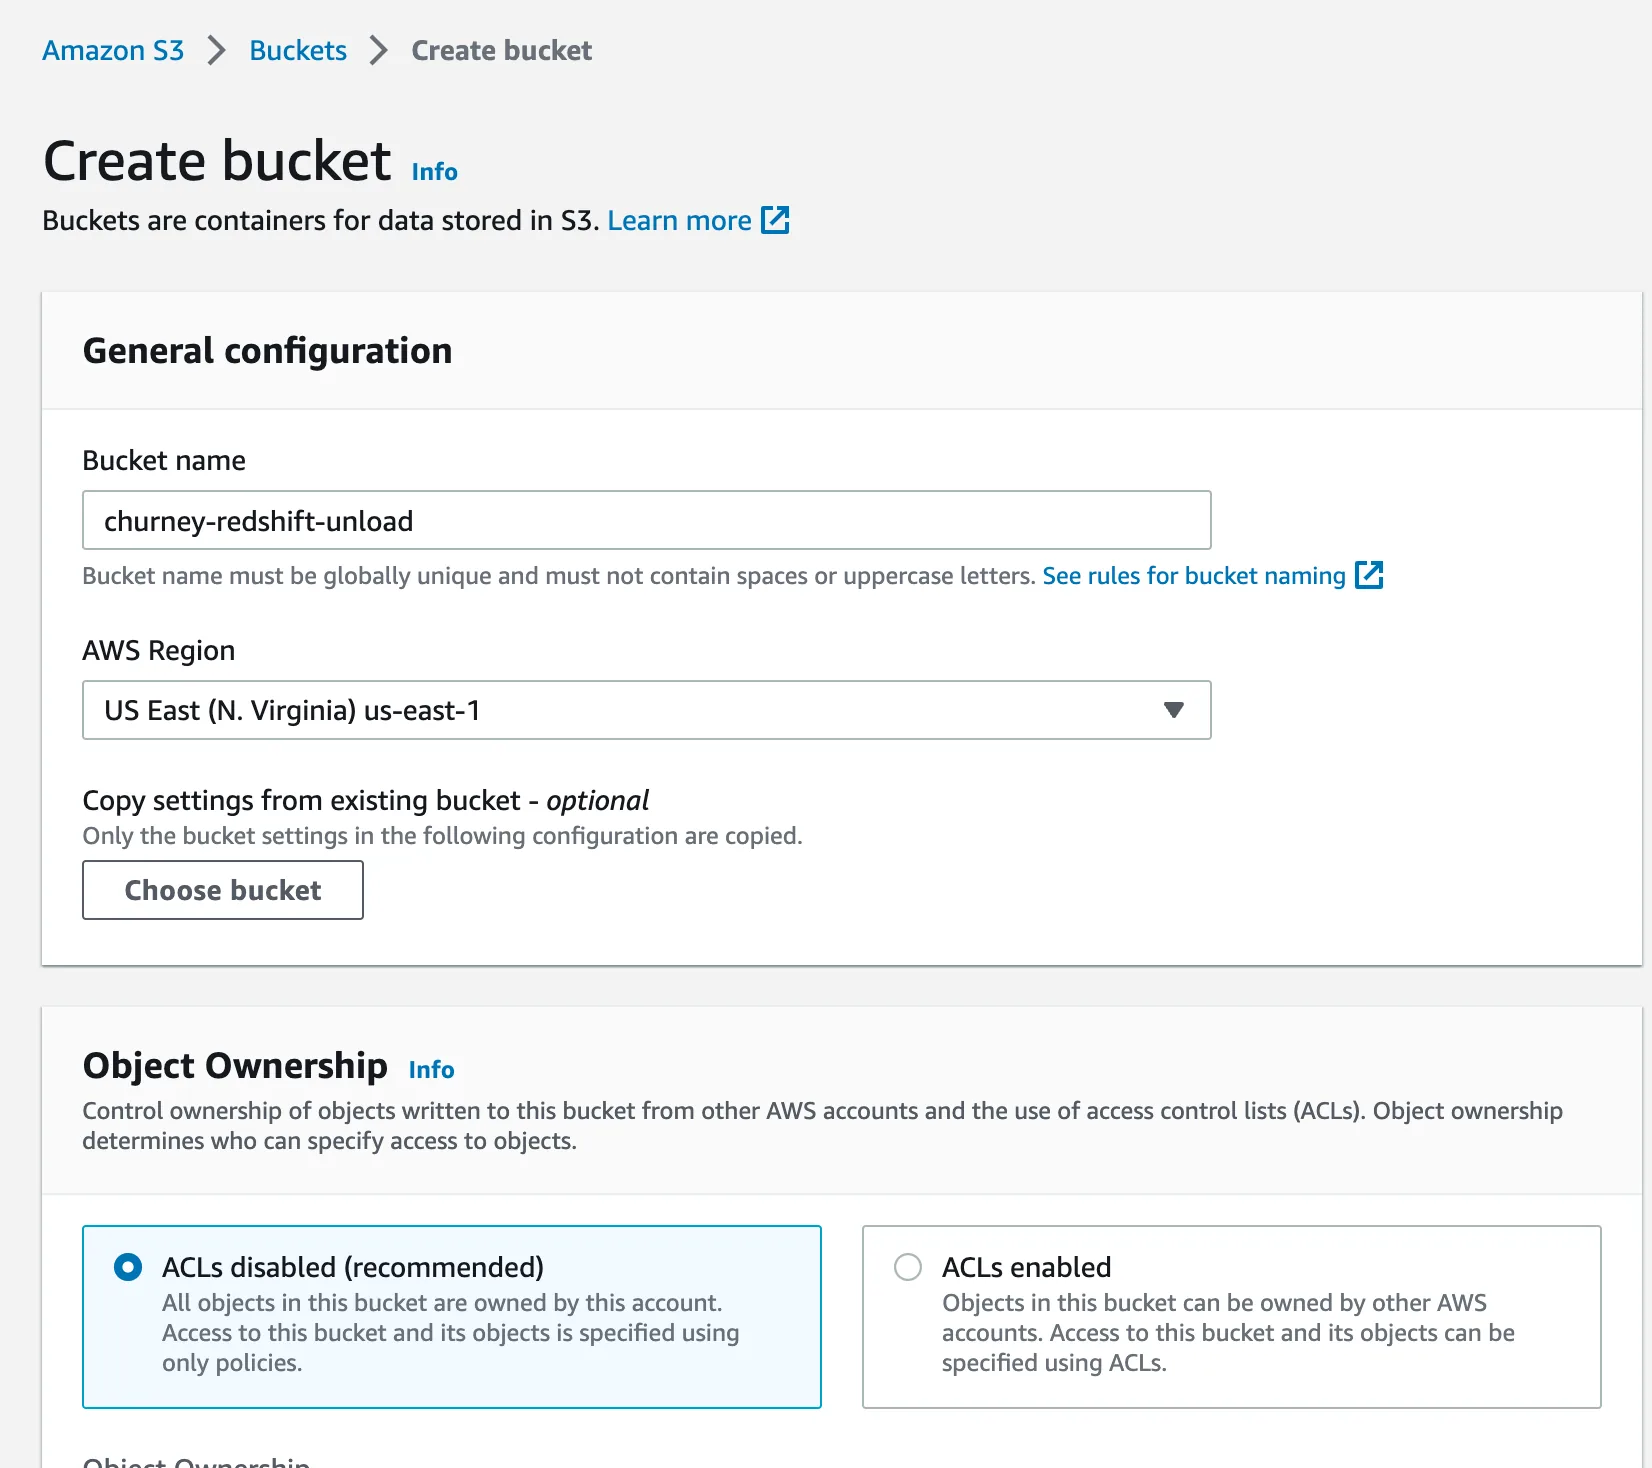
The bucket name
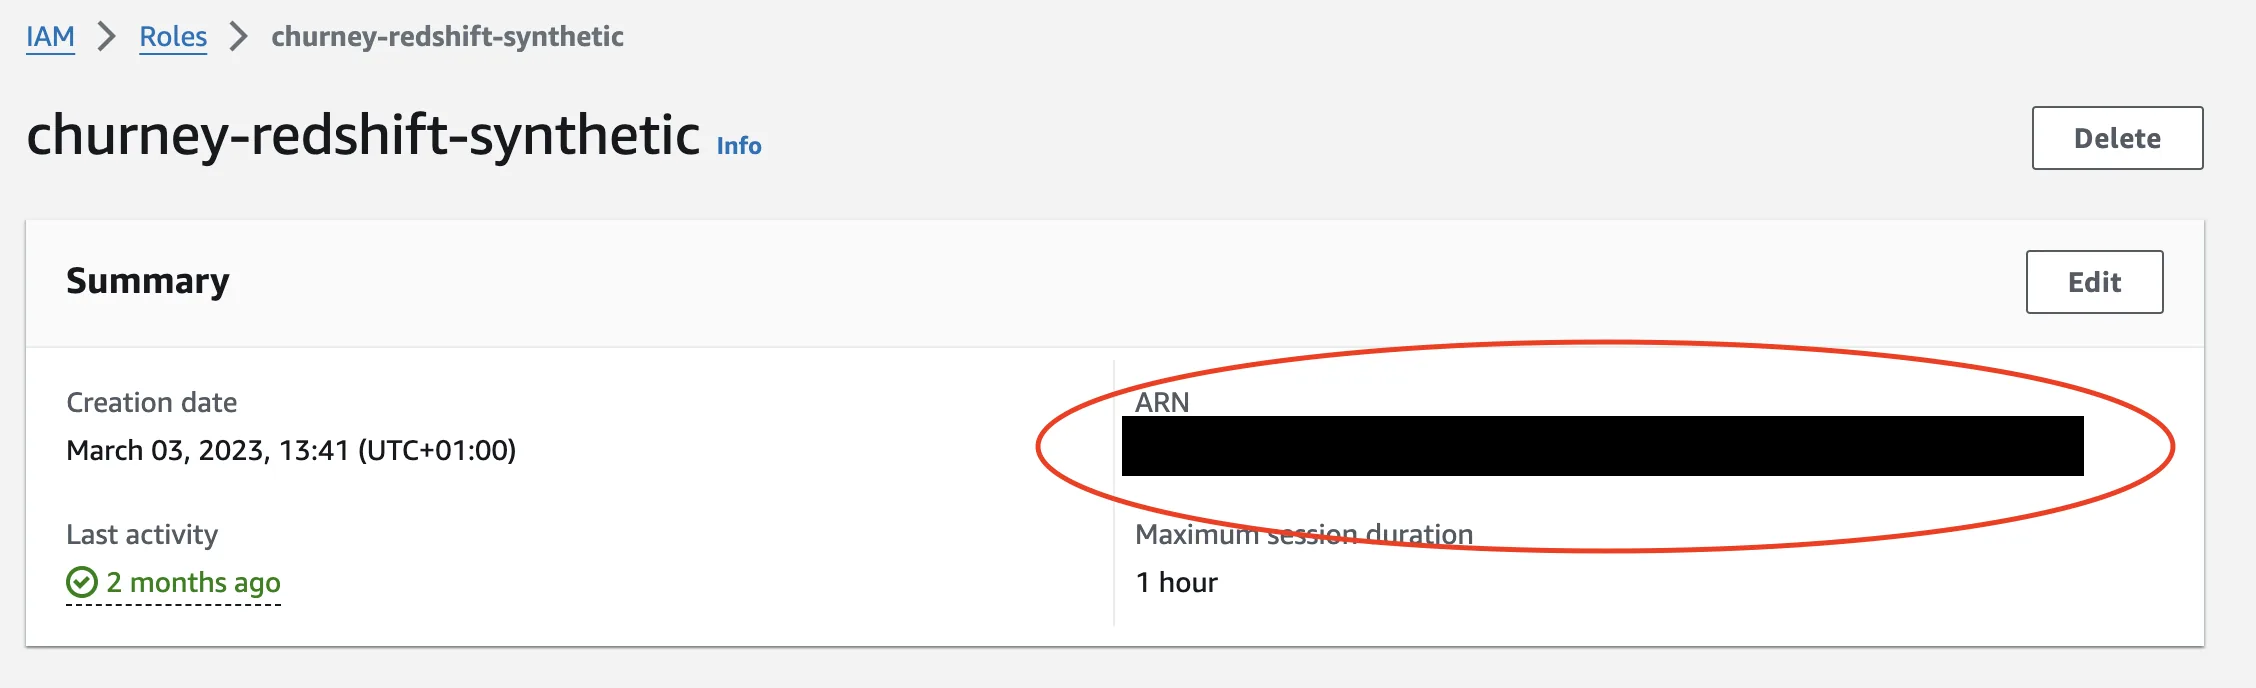
The role ARN
We take it from there.
What happens on our side
No action needed. This is here for your security review.
Read-only on your data. The churney user can select from the views in churney and nothing else.
No stored passwords. The user has no password. We get credentials for it per sync through the IAM role, which only Churney's Google identities can assume.
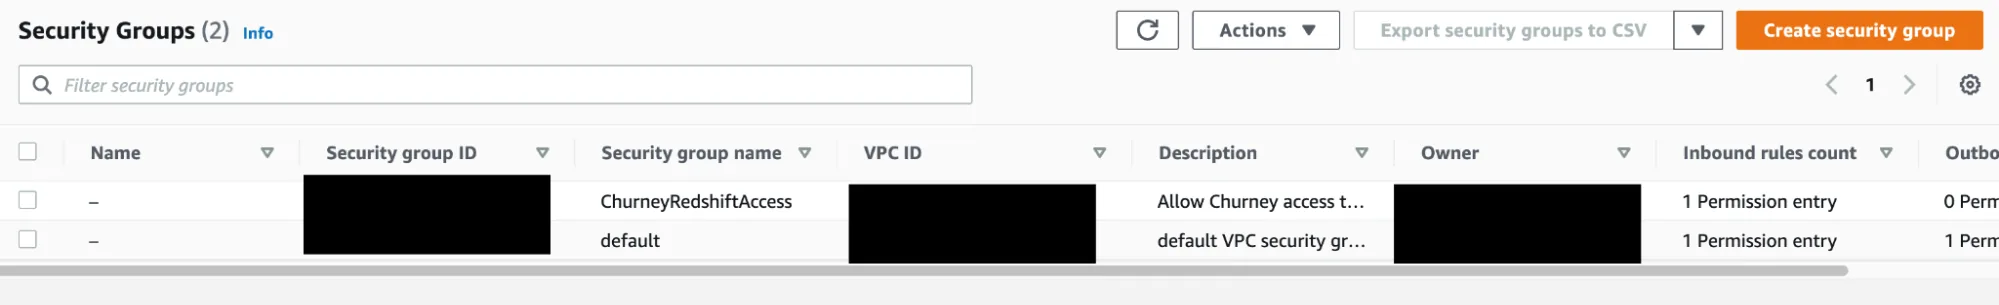
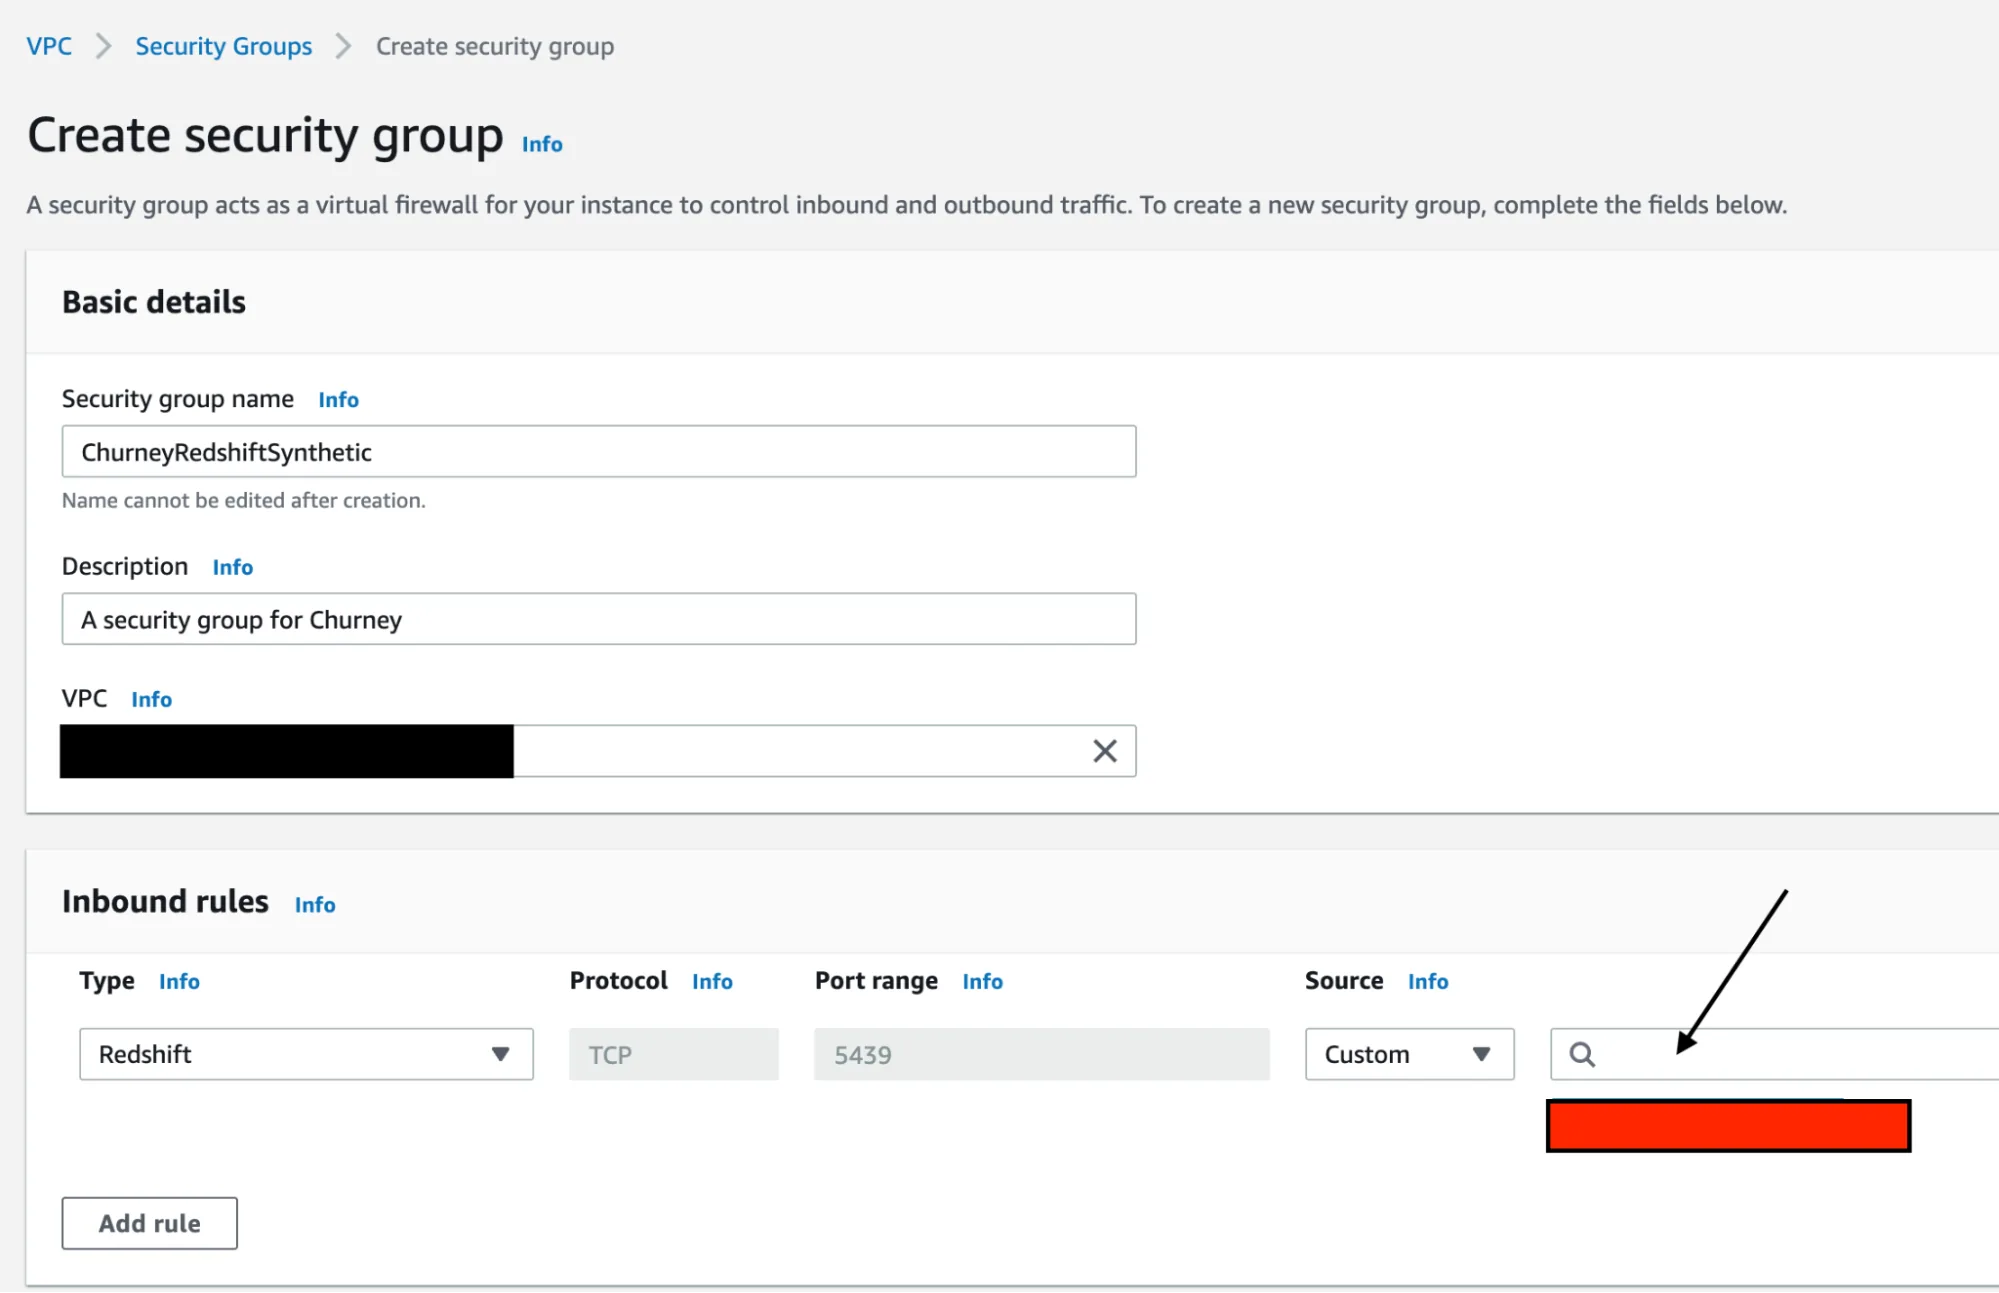
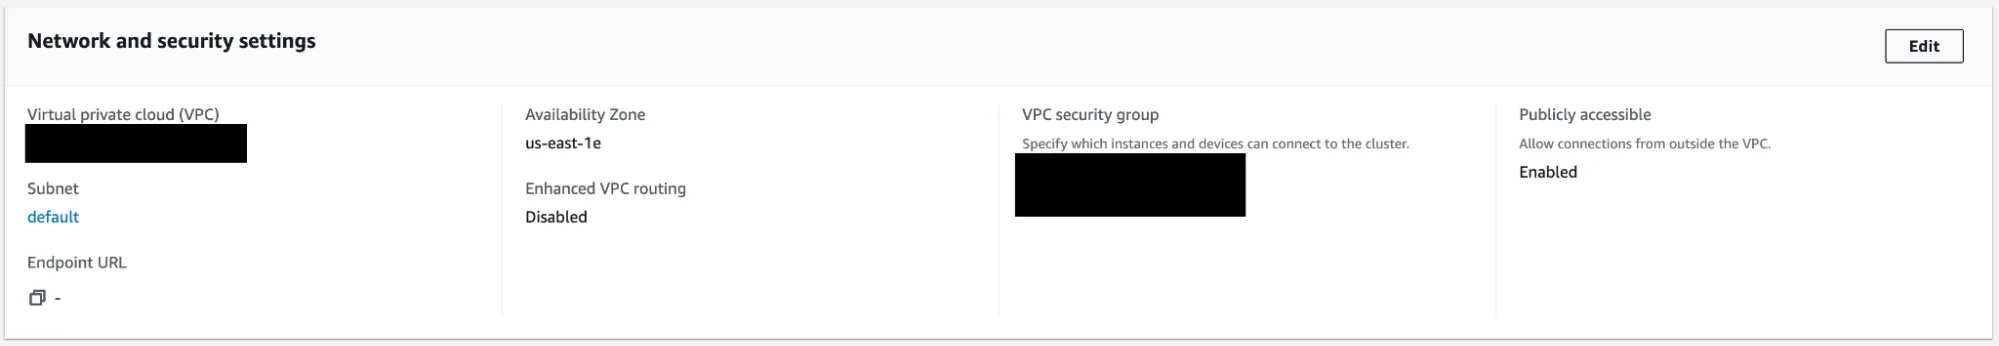
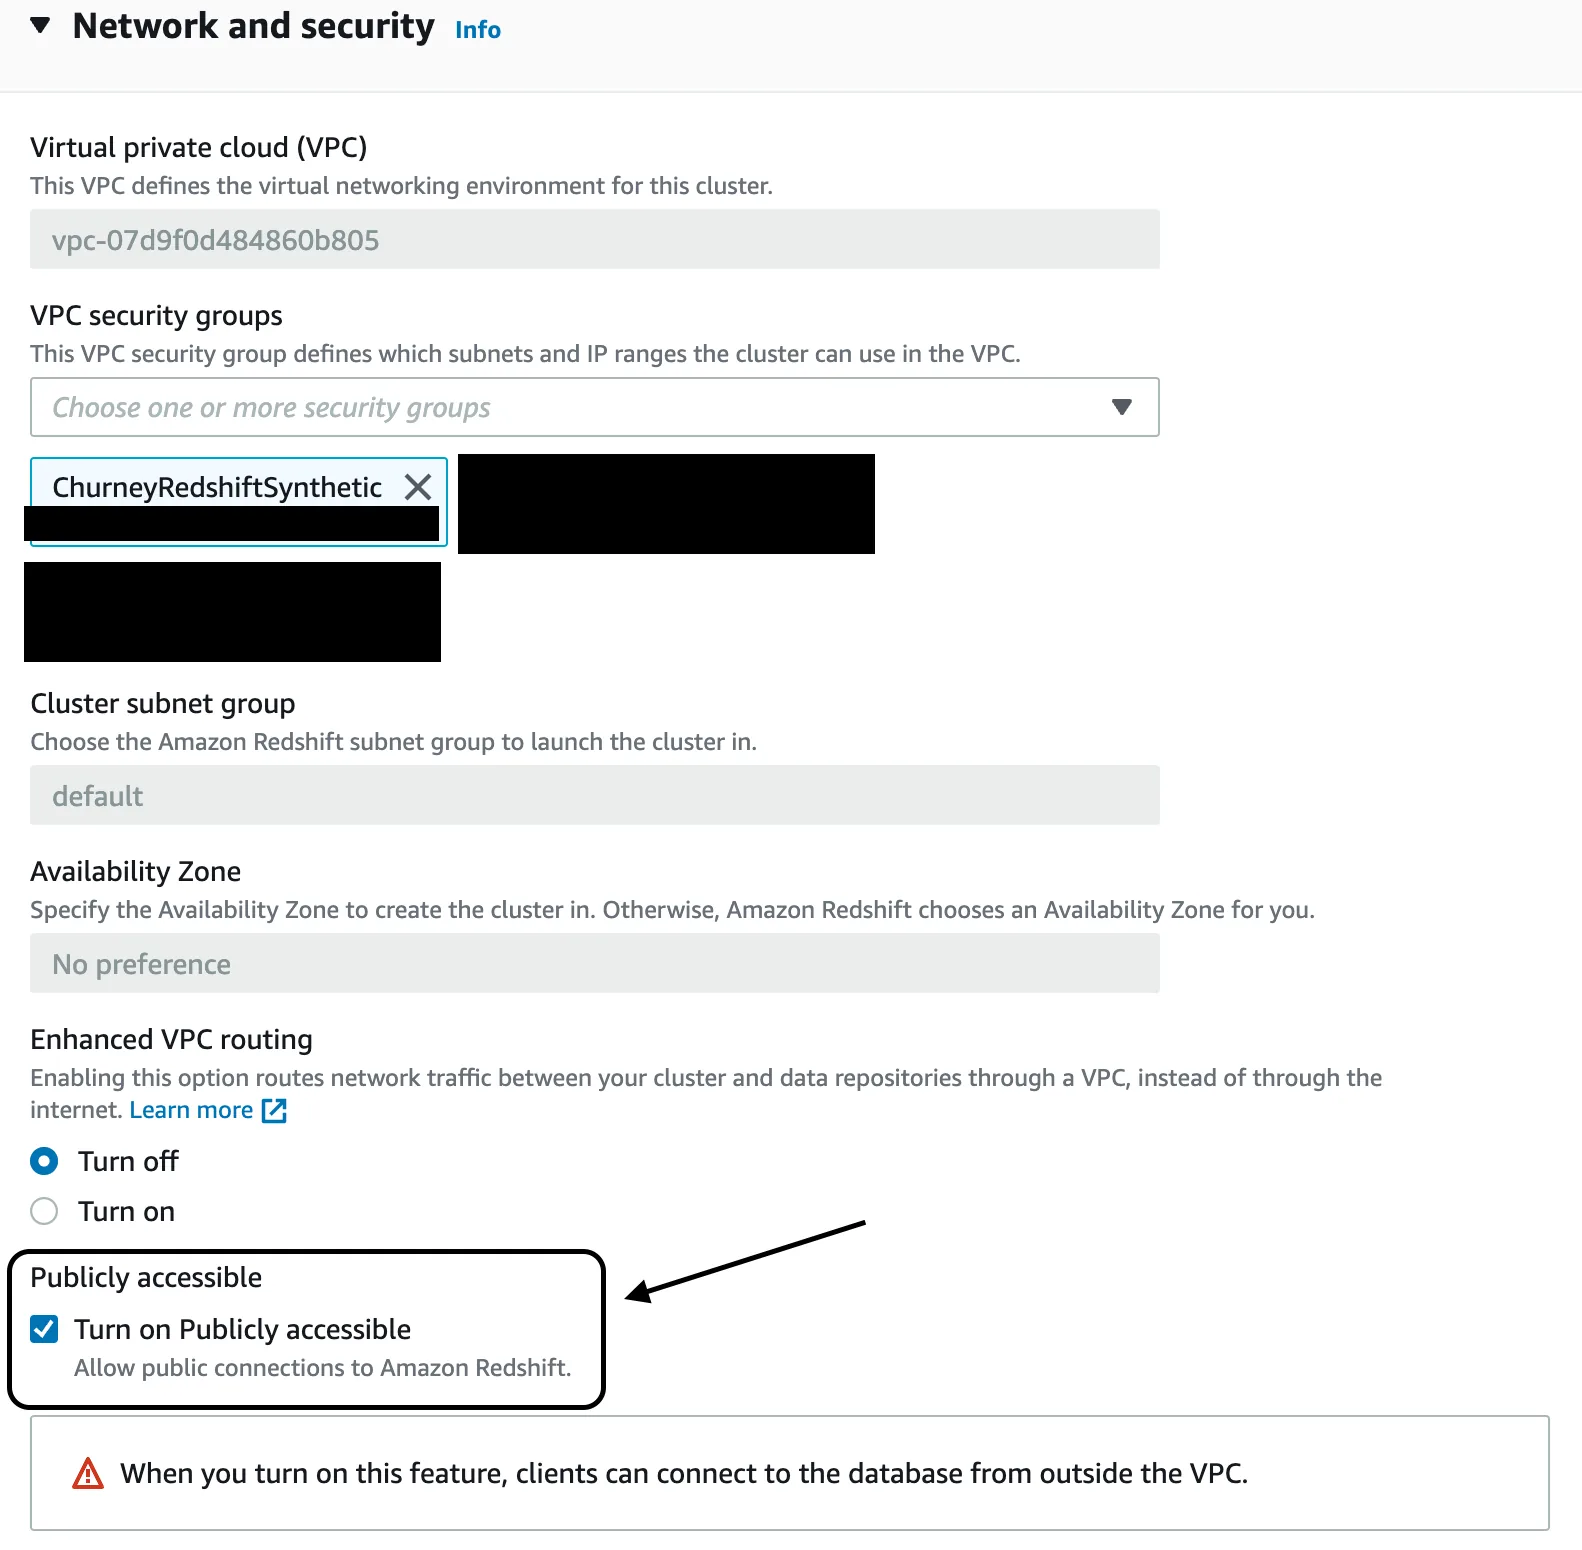
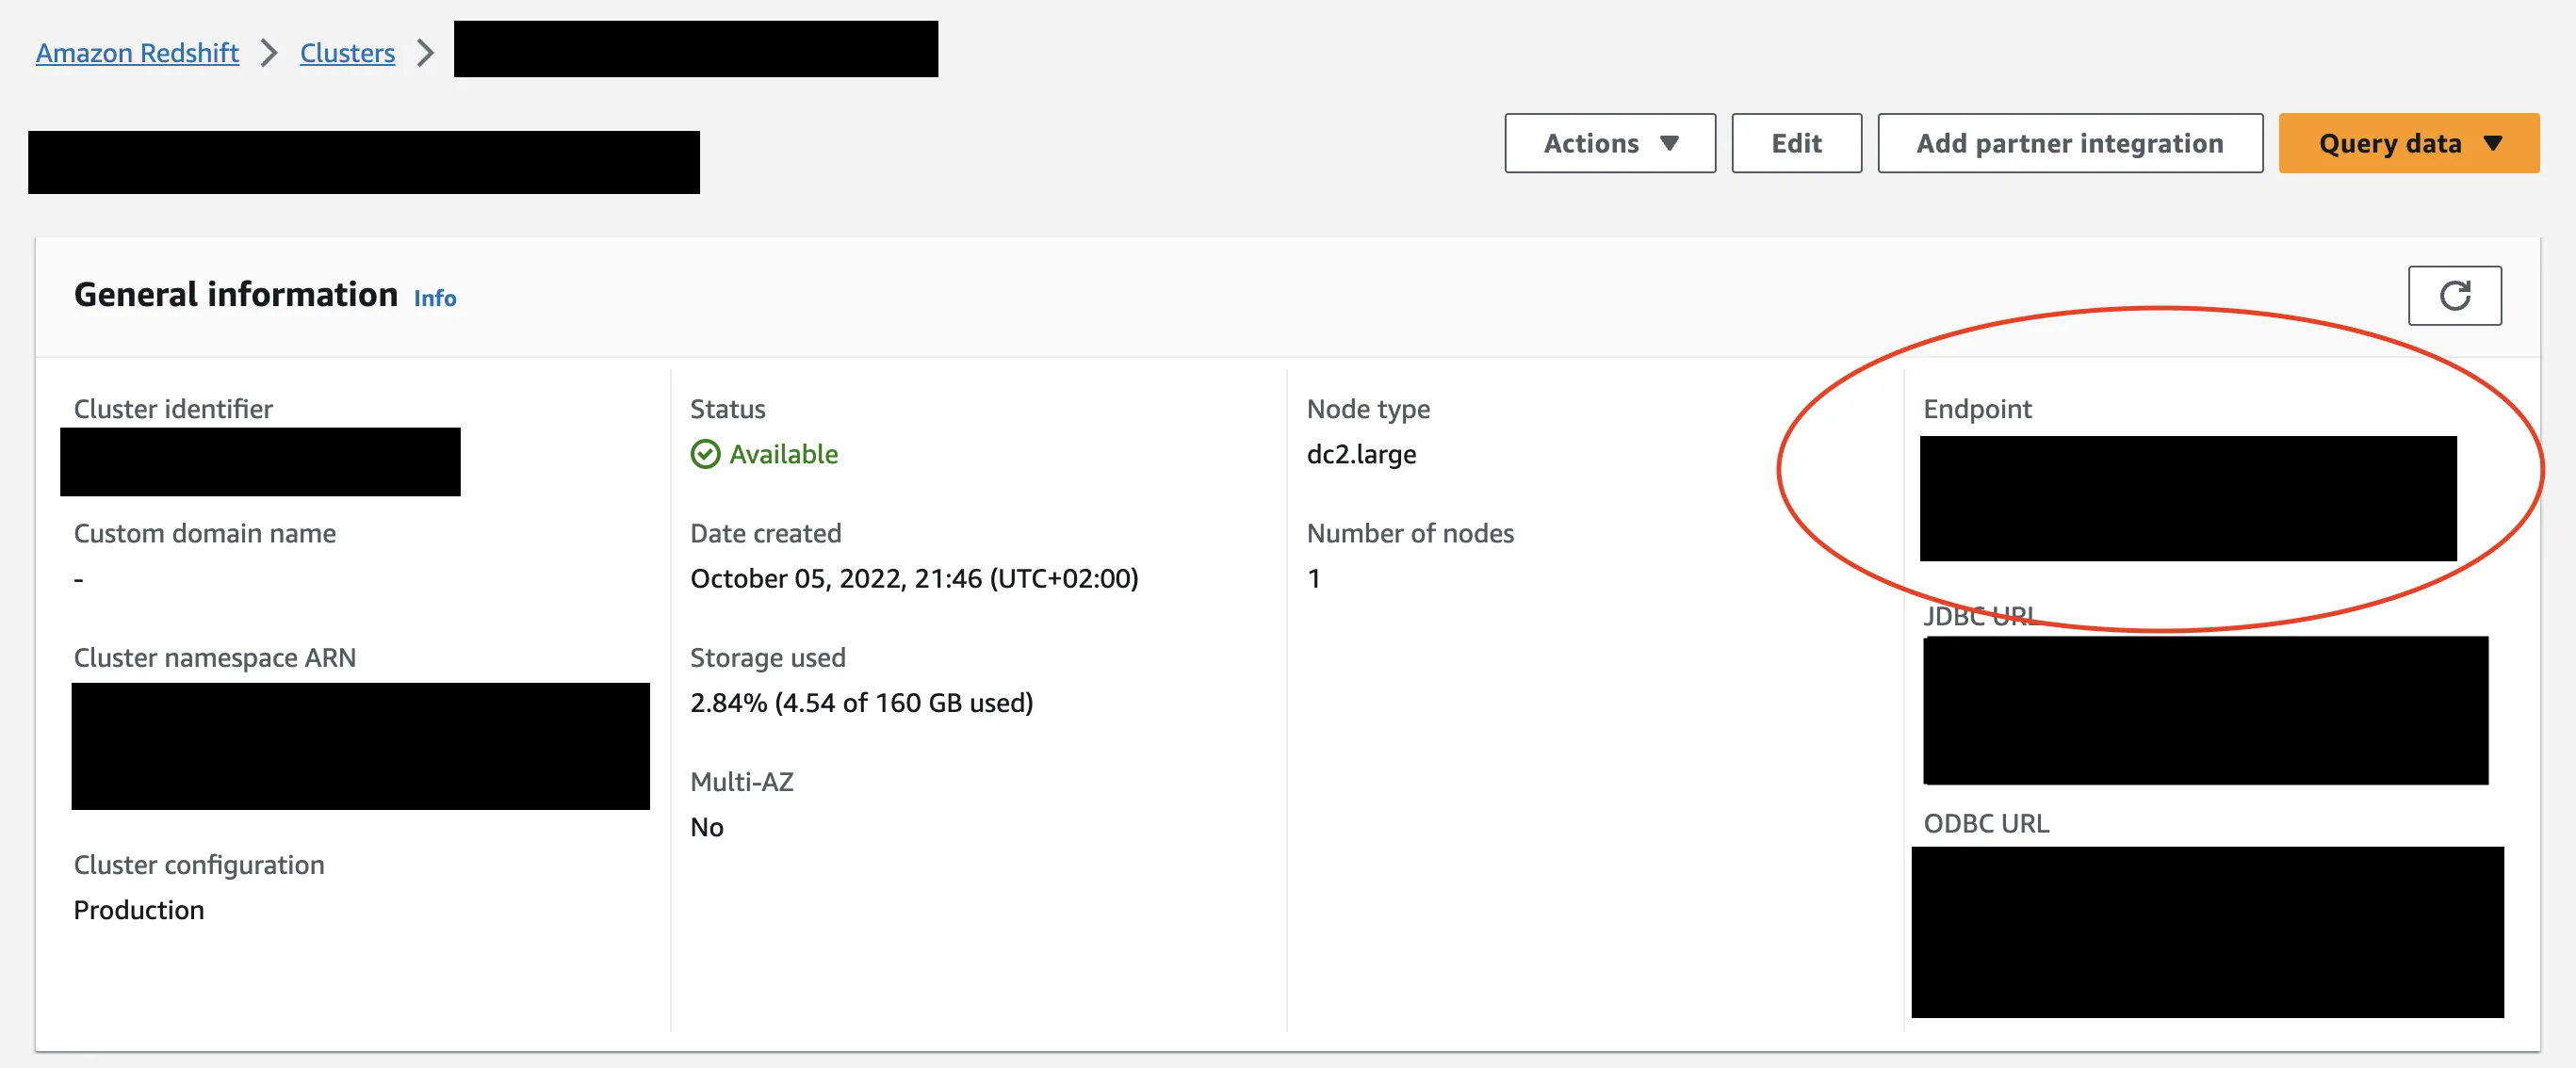
One door in. Only the Churney IP can reach the cluster through the security group you add.
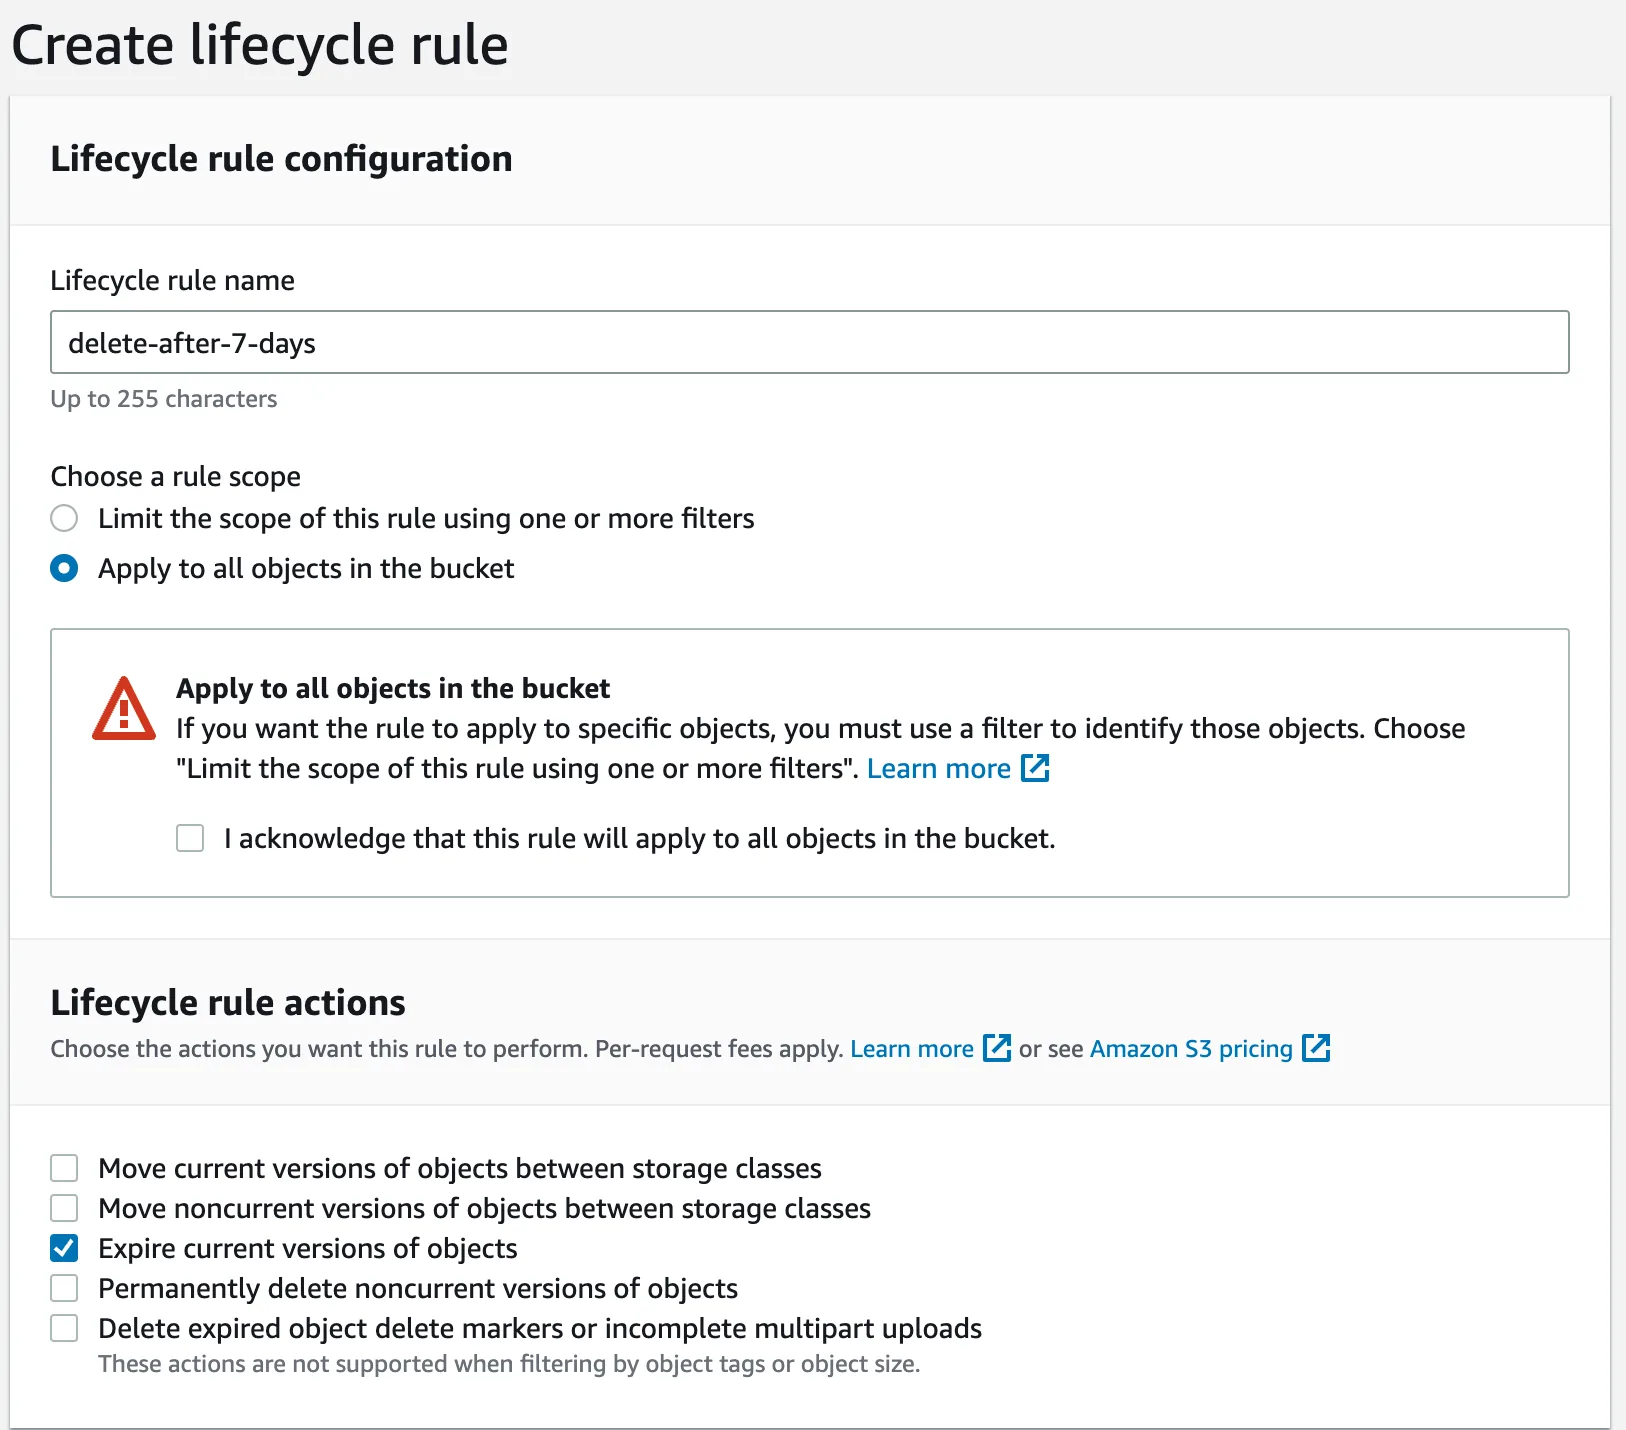
Direct, incremental export. We unload new or changed rows to your bucket as Parquet and copy them out. Files expire after 7 days.
 Read-only access. Identifiers hashed before anything leaves your warehouse.